Vercel Sandbox Adds Secure Compute Support for AWS VPC Peering and Dedicated IP Routing
Vercel Sandbox now supports Secure Compute, allowing preview environments to route outbound traffic through static IP addresses and securely peer with private AWS VPC resources.
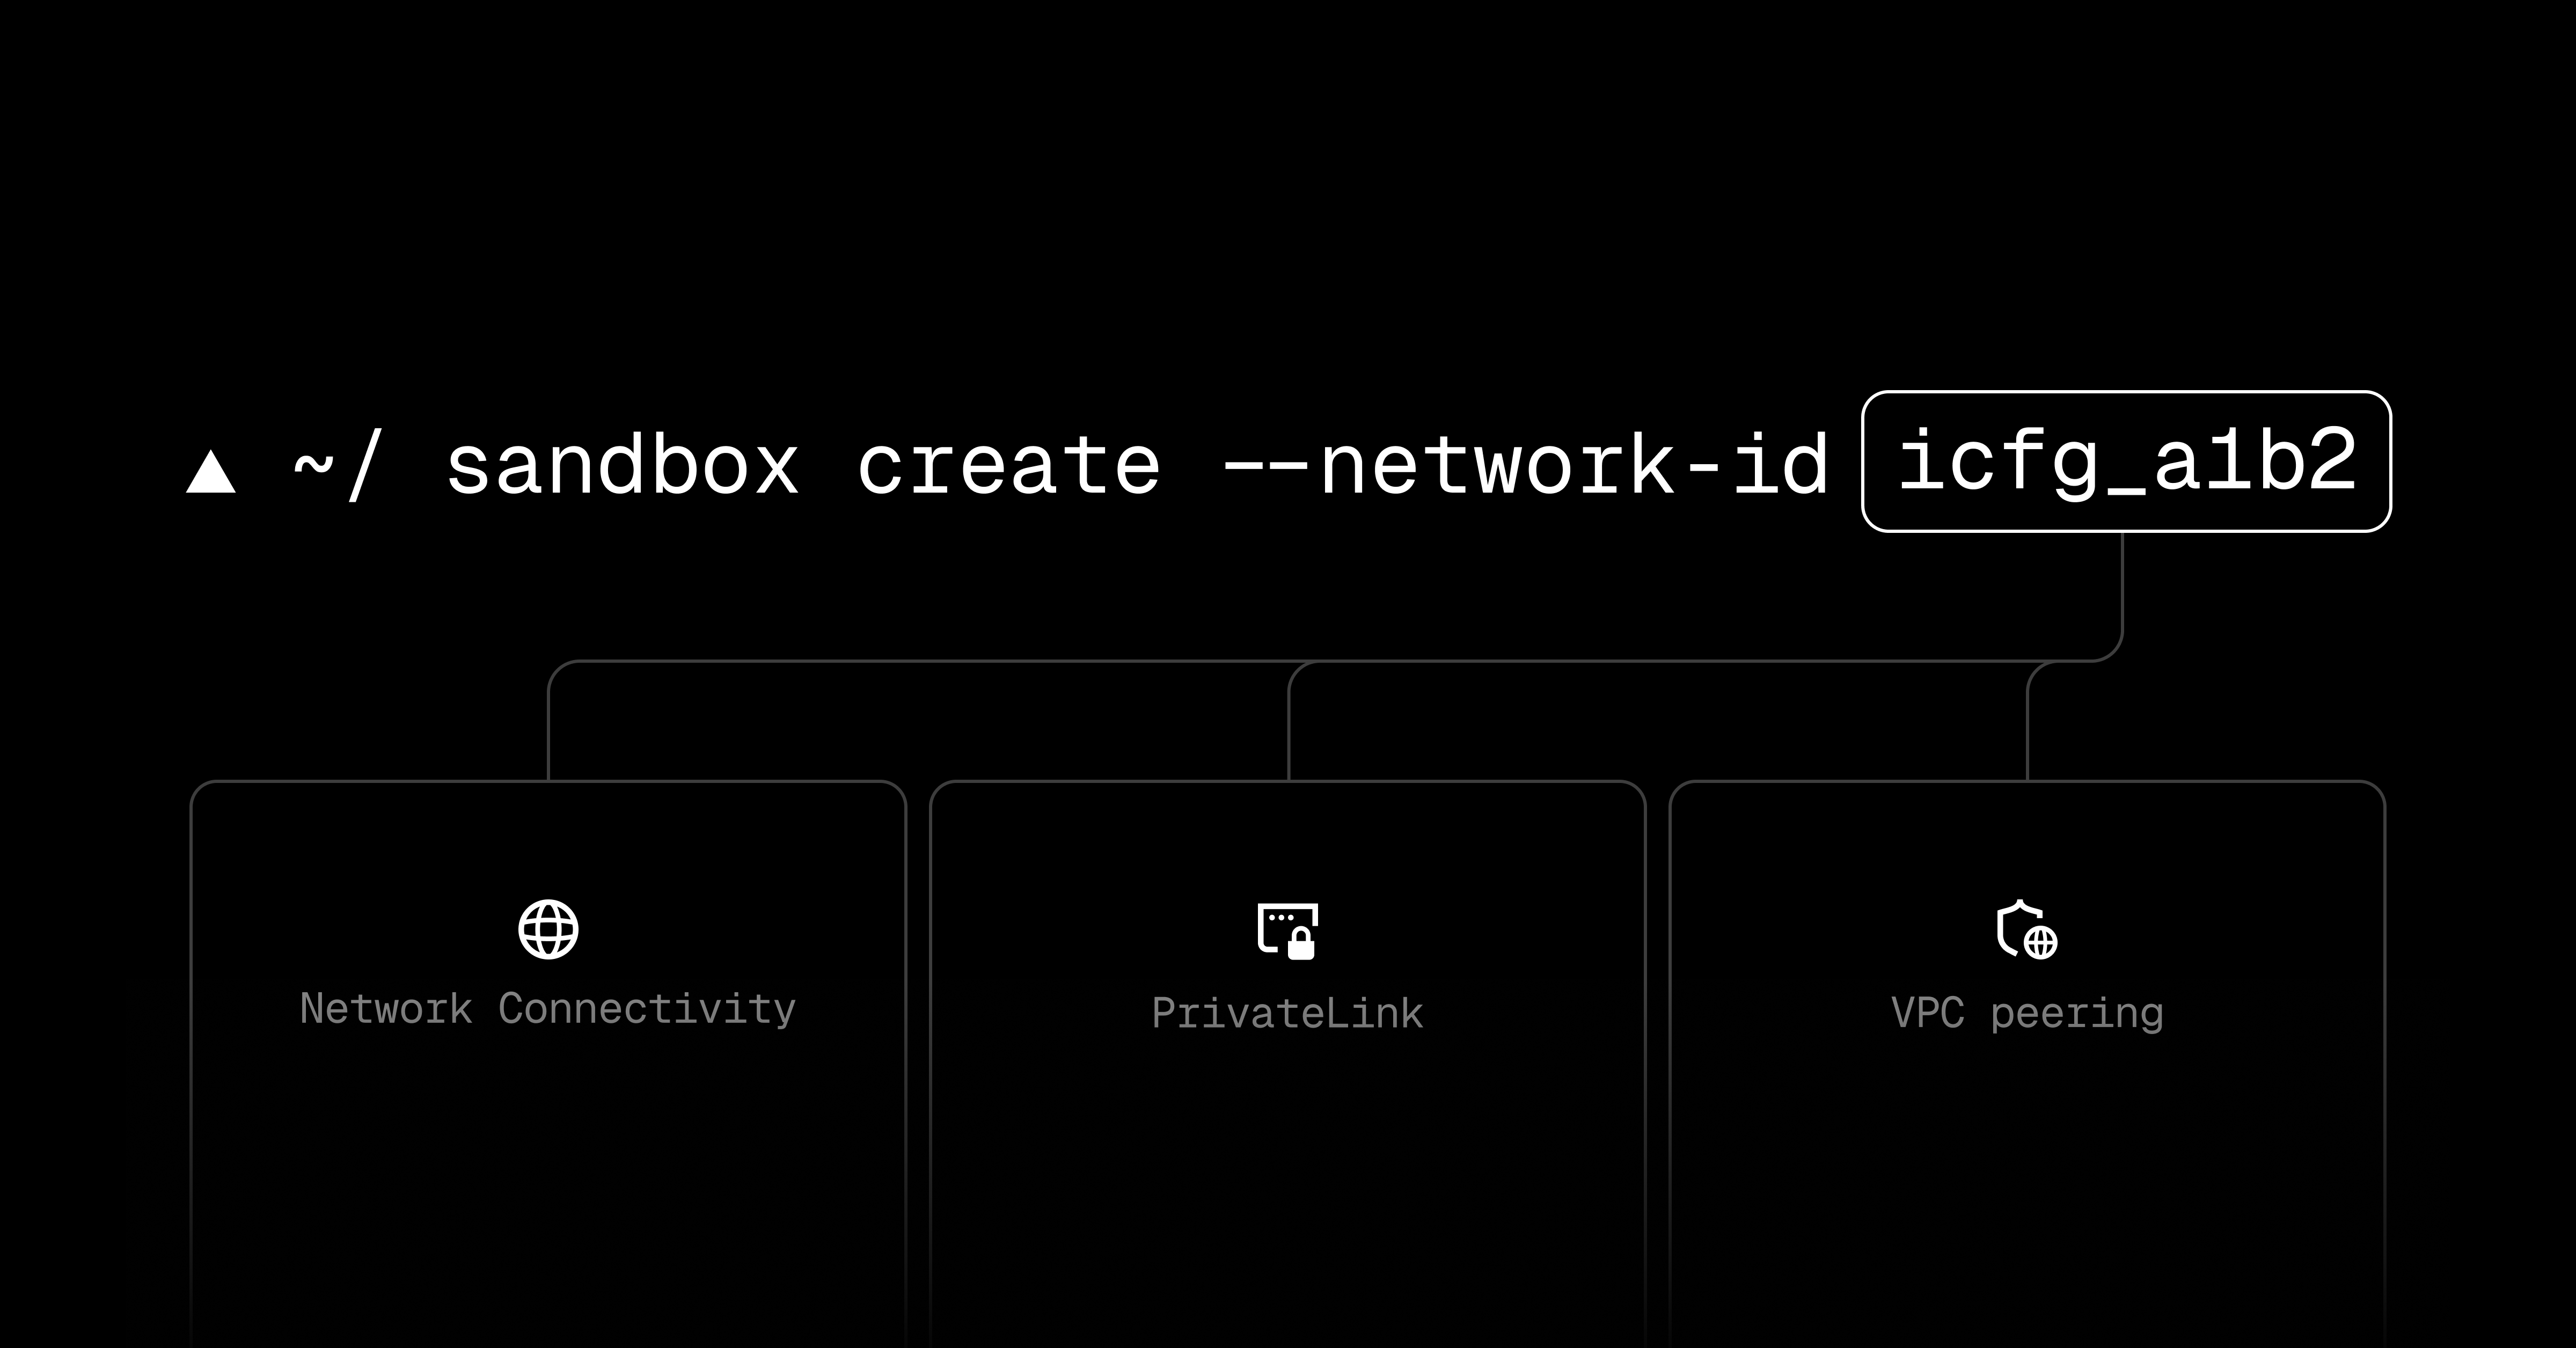
Vercel has integrated Secure Compute support into Vercel Sandbox, enabling teams to connect their sandbox environments to dedicated networks. Under this setup, all outbound traffic heading to the public internet is routed through designated static IP addresses. This update allows developers to easily bypass traditional IP-blocking restrictions on external APIs and databases during development and testing.
Primary source
Open Vercel Changelog ↗This article summarizes the source. Check the original for full details and conditions.
Comparison
| Aspect | Before / Alternative | After / This |
|---|---|---|
| Outbound IP Addresses | Dynamic IP addresses requiring complex proxy configurations | Dedicated static IP addresses routed through Secure Compute |
| AWS VPC Connectivity | No native peering, requiring exposure of databases to the internet | Direct private access to VPC resources via VPC peering |
| Sandbox Provisioning | Standard CLI creation without network isolation parameters | CLI creation using the --network-id flag for secure networks |
Action Checklist
- Enable the Vercel Secure Compute add-on in your account This is a prerequisite for routing Sandbox traffic through dedicated networks.
- Provision new Sandboxes with the network ID flag Use the CLI command 'sandbox create --network-id <id>' to link the network.
- Update existing Sandbox network settings using sandbox.update() Remember that active sessions will retain their current settings until they are stopped and restarted.